How self-healing browser sessions preserve authenticated coverage through recorded login flows, fresh authentication challenges, and validation across tabs and isolated browsers.
Suppose a security researcher signs in, starts interacting with an application, and runs an automated assessment. Everything works initially. Later, the session expires. Requests that previously reached account settings, internal workflows, or authenticated APIs now reach a login page.
The application still responds. The worker is still running. The assessment may still look busy. But its authenticated coverage has changed.
A login page can even return HTTP 200. If the assessment treats that response as evidence that it reached the intended functionality, it can quietly miss entire areas of the application. Authentication failures can also be mistaken for application behavior, weakening the conclusions drawn from a test.
A human researcher notices the logout and signs back in. An autonomous assessment needs to recognize the same interruption, restore access, and establish that it is working under the intended identity again.
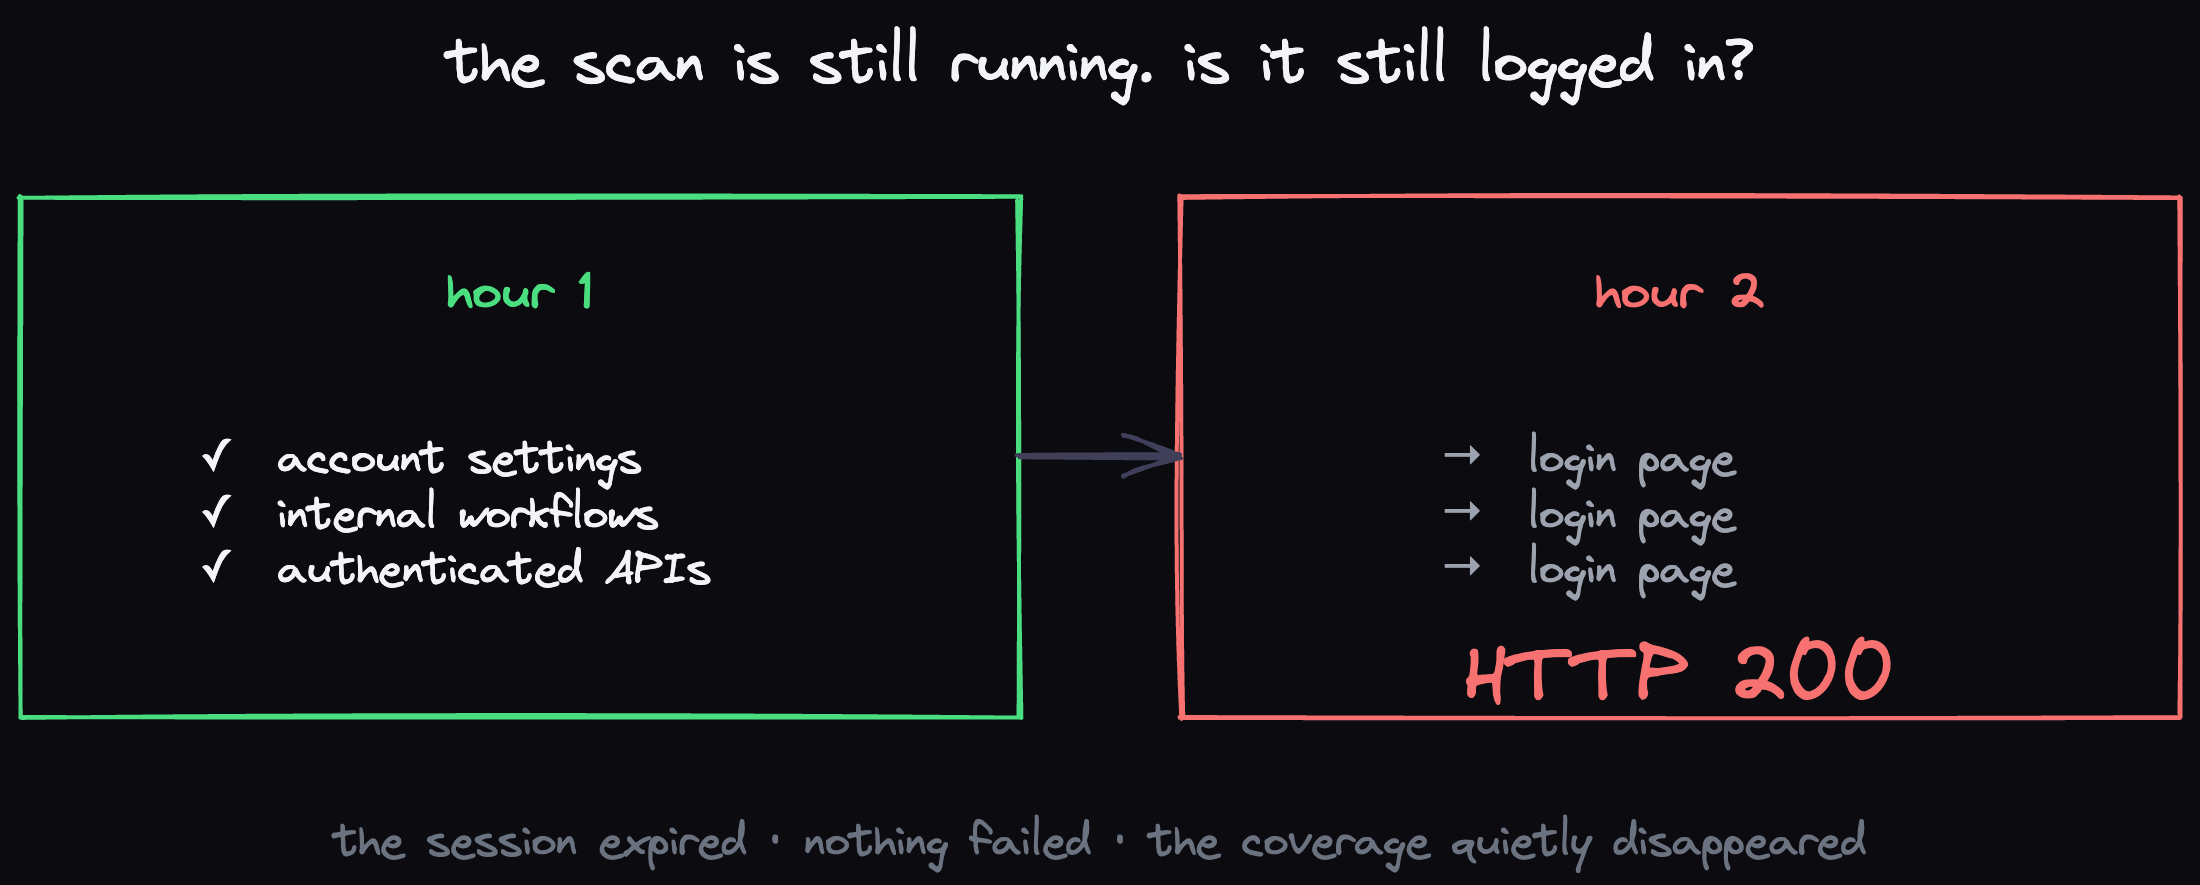
The session expired. Nothing failed. The authenticated coverage quietly disappeared.
A browser session is the state that lets an application recognize a signed-in user across requests and page visits. Cookies and browser storage can carry that state. As the user moves through the application, the session connects those interactions to an identity and its permissions.
For autonomous testing, saving this state is only the beginning. Sessions expire, tokens rotate, and applications invalidate logins. An assessment that depends on a single captured cookie inherits its lifetime.
Pentest Copilot pairs the authenticated browser state with a recorded login flow and evidence of what successful authentication looks like. Together, they give the agent a way to recognize lost access and restore it.
At validation points during an assessment, the agent checks the session against that evidence. When authentication is lost, it replays the recorded flow, obtains fresh state, and verifies the result before accepting the recovered session.
Capture the login → establish the authenticated baseline → detect lost access → replay → verify.
The value is continuity: authenticated work can continue without requiring a researcher to keep returning to the login screen.
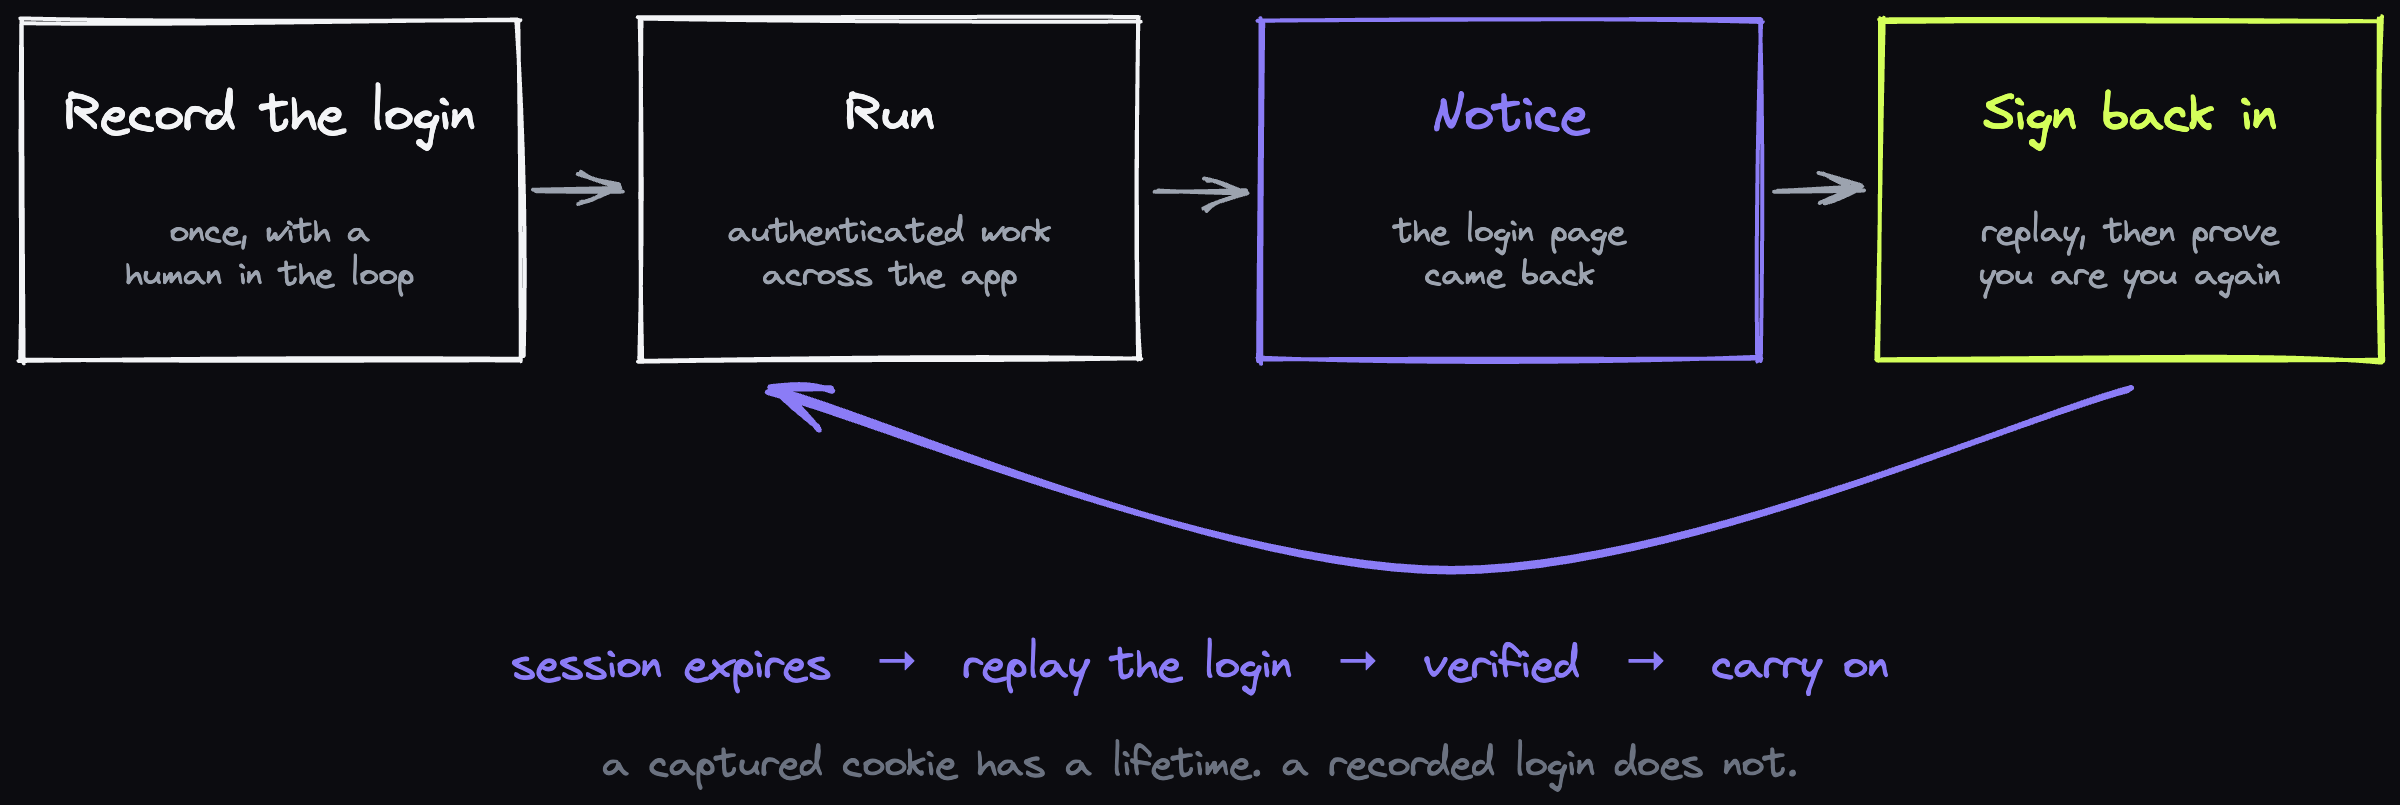
A captured cookie has a lifetime. A recorded login does not.
The recording captures the browser interactions that lead to a successful login, alongside the resulting session state. It also preserves a verification URL and the expected evidence on that page. Completing the recorded actions and proving that the browser is authenticated are separate requirements.
The Browser Session Manager adds context around that recording: which account is being used, what it can access, its role tags, the monitored email identity, and where the browser runs. That context helps distinguish identities and interpret privilege boundaries during an assessment.
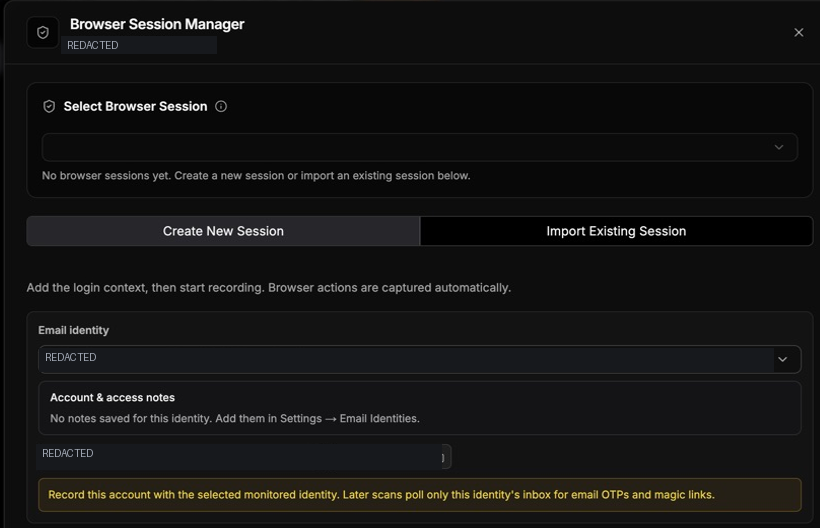
The manager associates the recording with an account context and monitored authentication identity.
Recording and assessment should use consistent browser egress. A change in region or network origin can change how an application treats a session, even when the credentials remain valid.
Authentication often includes a challenge that changes on every login. A reusable recording must handle the current challenge instead of submitting a value captured earlier.
| Authentication method | How the session handles it |
|---|---|
| TOTP | Generates a fresh time-based code using the configured authenticator secret. |
| Email OTP | Retrieves the current code from the selected monitored email identity. |
| Email magic link | Retrieves and opens the new sign-in link for the authentication attempt. |
| CAPTCHA | Automatically detects and solves supported CAPTCHA challenges encountered during the flow. |
The recorded flow preserves what needs to happen at each authentication stage. Fresh codes and links supply the values required for the current attempt. The authenticated-state check then confirms the outcome.
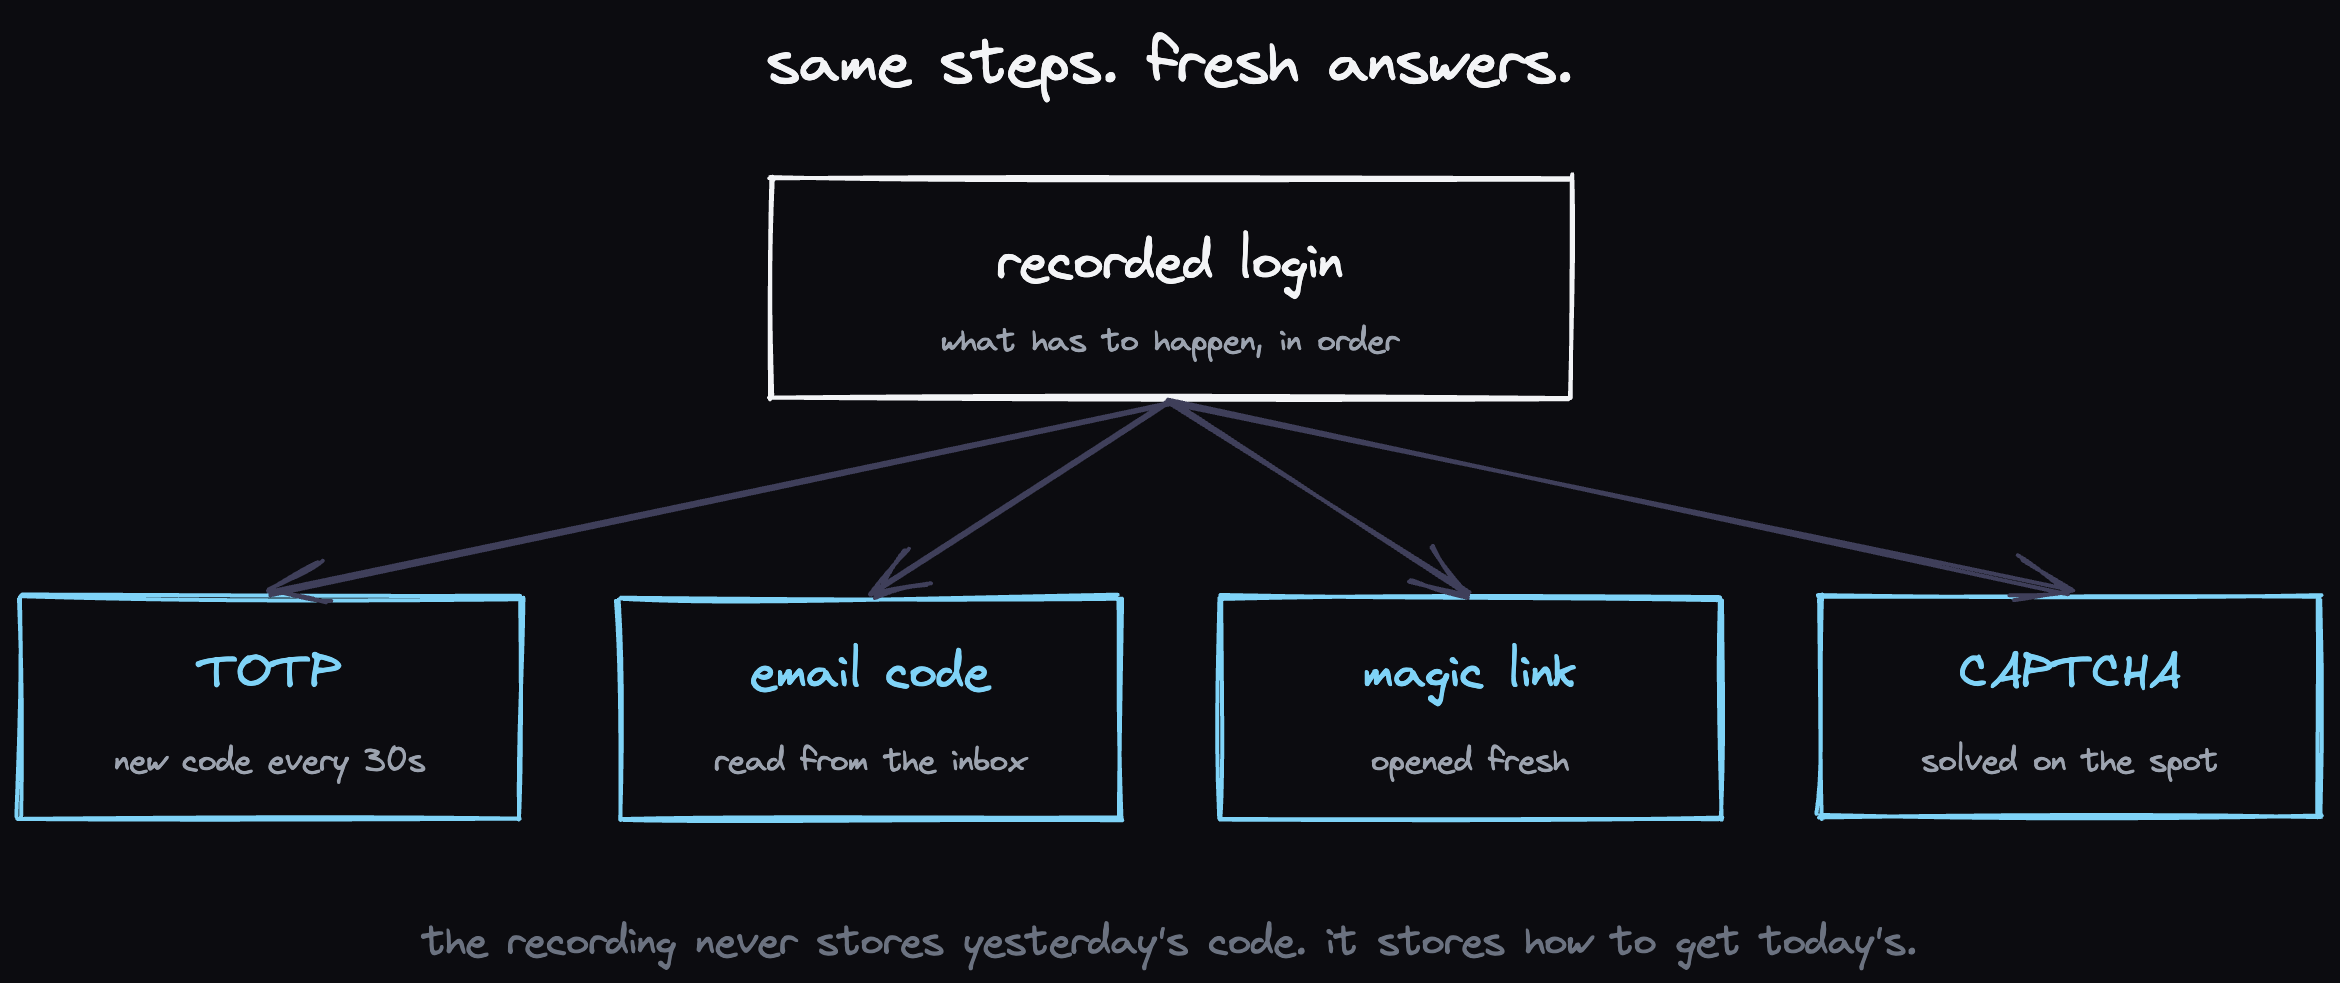
The recording never stores yesterday's code. It stores how to get today's.
BugBase, our bug bounty platform, provides a concrete example. The supplied recording follows a user from the login screen to authenticated account settings. The recorder highlights interactive elements and captures the login interactions.
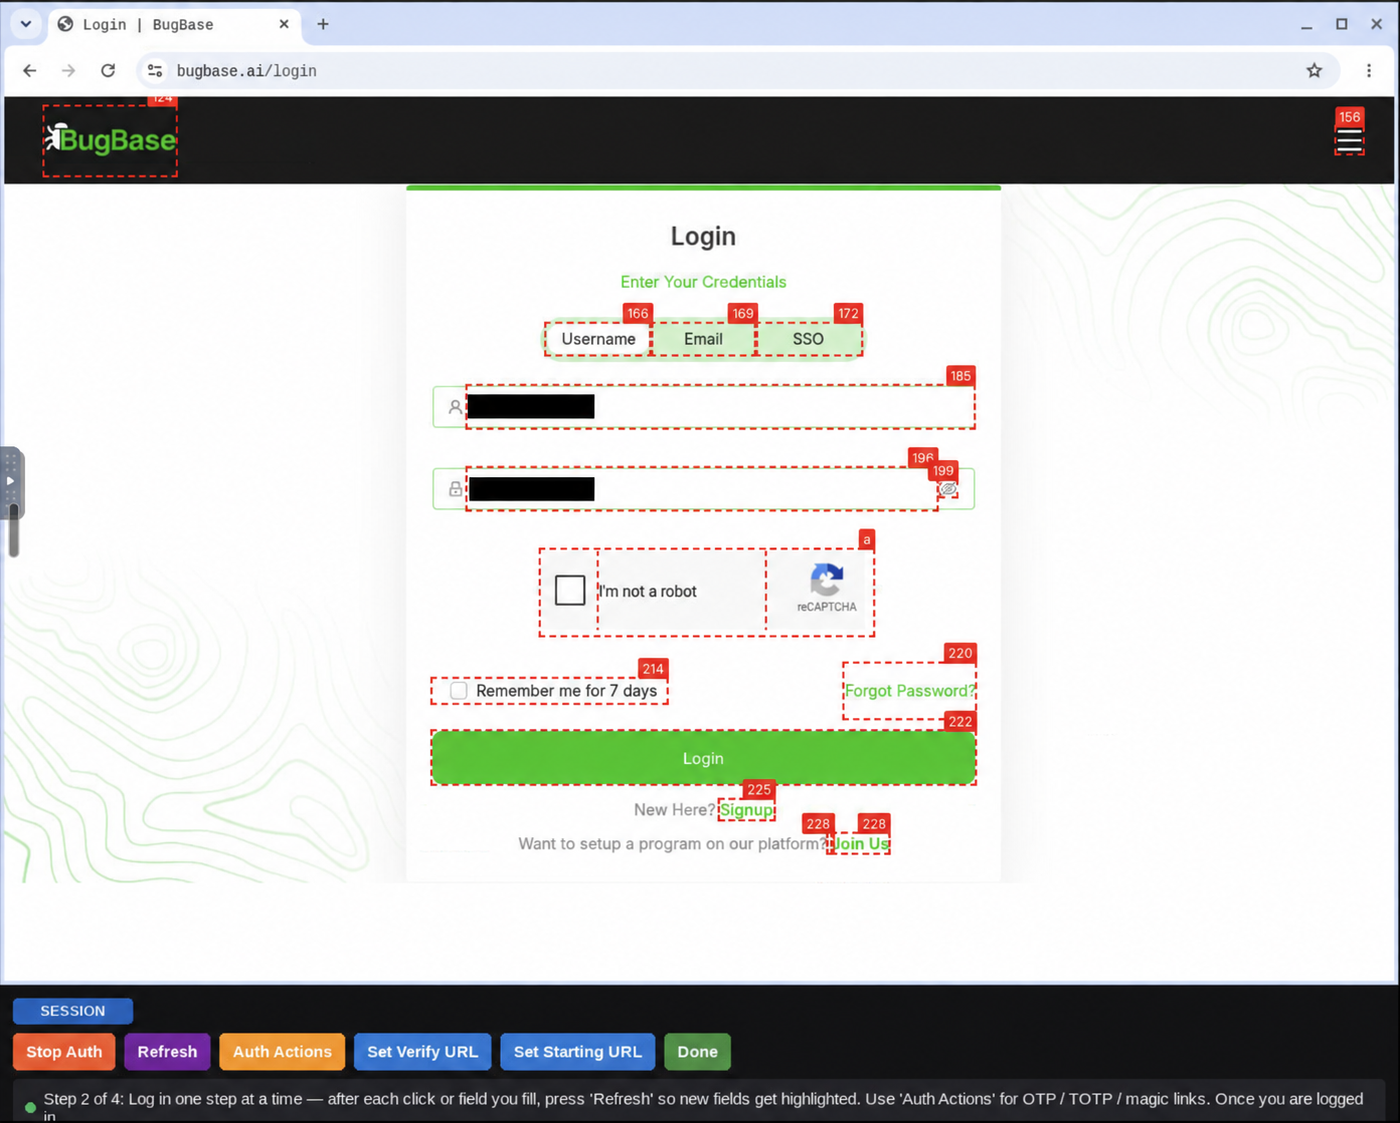
Login recording in progress. The recorder's highlighted elements show the page interactions being captured.
In this recorded flow, CAPTCHA detection and solving happened automatically. The checkbox appears unchecked in this frame; its appearance in a single screenshot does not represent the completed authentication outcome.
After login, the user's settings page provides a stable place to verify access. For this example, the authentication verification URL is https://bugbase.ai/dashboard/settings, and the keyword regex is Account Details.
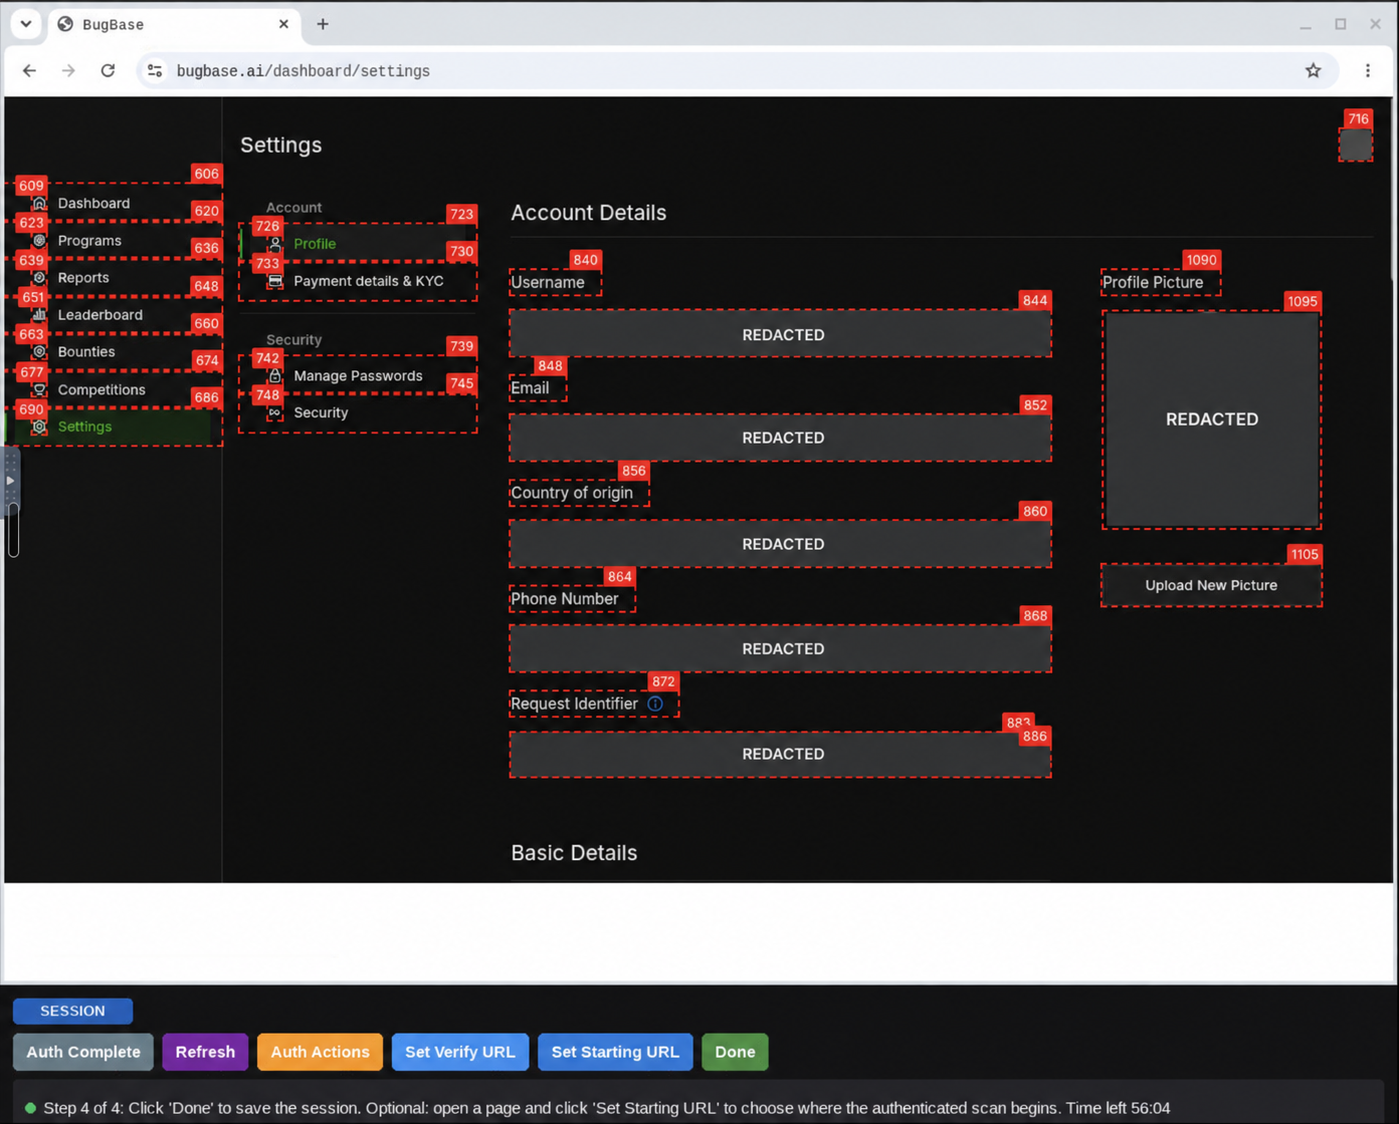
The settings page supplies the verification target. “Account Details” remains visible while account-specific values are redacted.
The verification target answers a specific question: did the browser reach the expected authenticated page? A public page that looks identical before and after login would not establish that distinction. The verification page can also differ from the starting page used for the assessment.
For example, authenticated testing could subsequently examine a report workflow. Any resulting bug report needs to describe the active role, expected access boundary, and observed behavior. Recovering the session preserves the identity context needed to interpret that evidence; it does not itself establish a vulnerability.
Finishing the recording is followed by session validation. A login that works in the original tab may depend on state that does not carry into another tab or browser. A saved session may also work today while its recorded recovery flow fails.
The validation checks address these different dependencies:
| Check | What it establishes |
|---|---|
| Authenticated check | The captured session reaches the expected authenticated state. |
| Unauthenticated check | The same verification distinguishes a logged-out browser from a logged-in one. |
| Replay test | The captured login actions can recreate authenticated access. |
| Parallel-tab test | The session remains usable across multiple tabs at the same time. |
| Parallel-login test | Authentication works across two isolated browser contexts. |
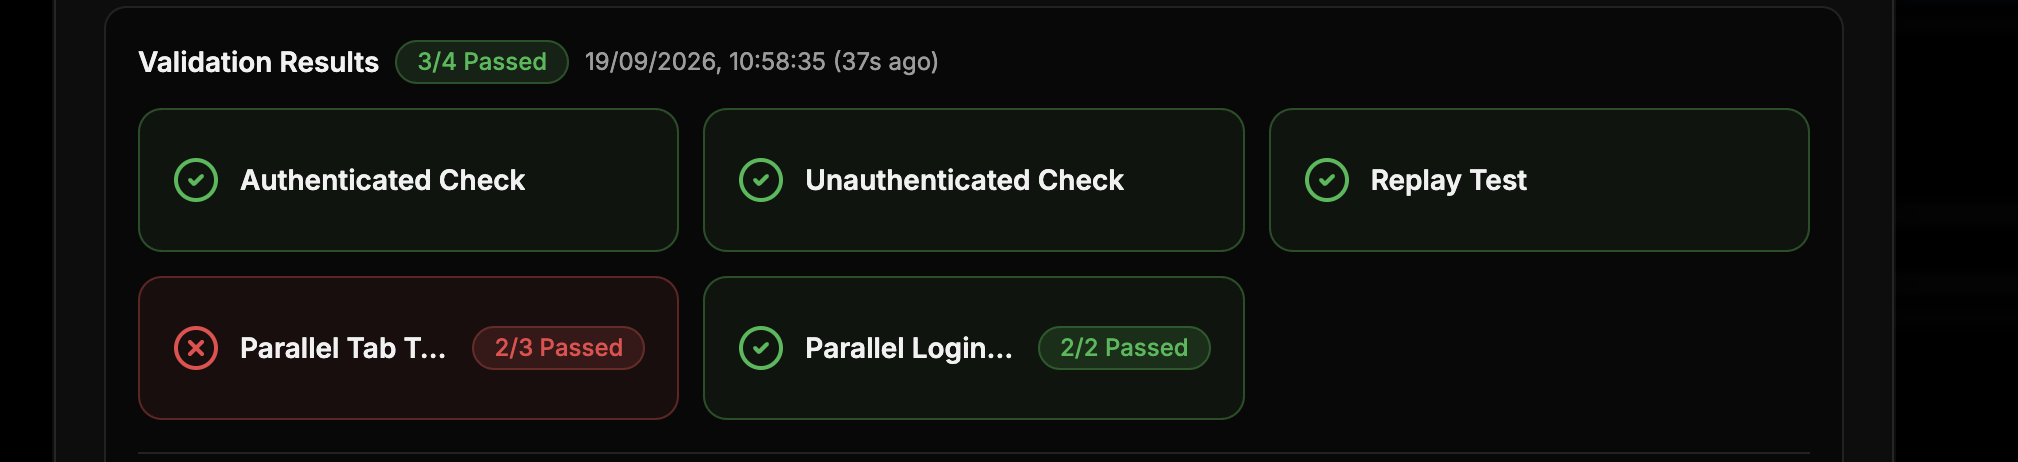
This capture shows replay passing and parallel login at 2/2. Parallel tabs passed 2/3, so this result does not establish full parallel-tab readiness.
The partial result is useful information. It distinguishes “we can sign back in” from “every concurrent browser context can use this session.” The screenshot alone does not establish why one tab failed.
Self-healing depends on both recovery and reuse. Validation exposes where either breaks, before the assessment relies on a recording to maintain authenticated access across its work.
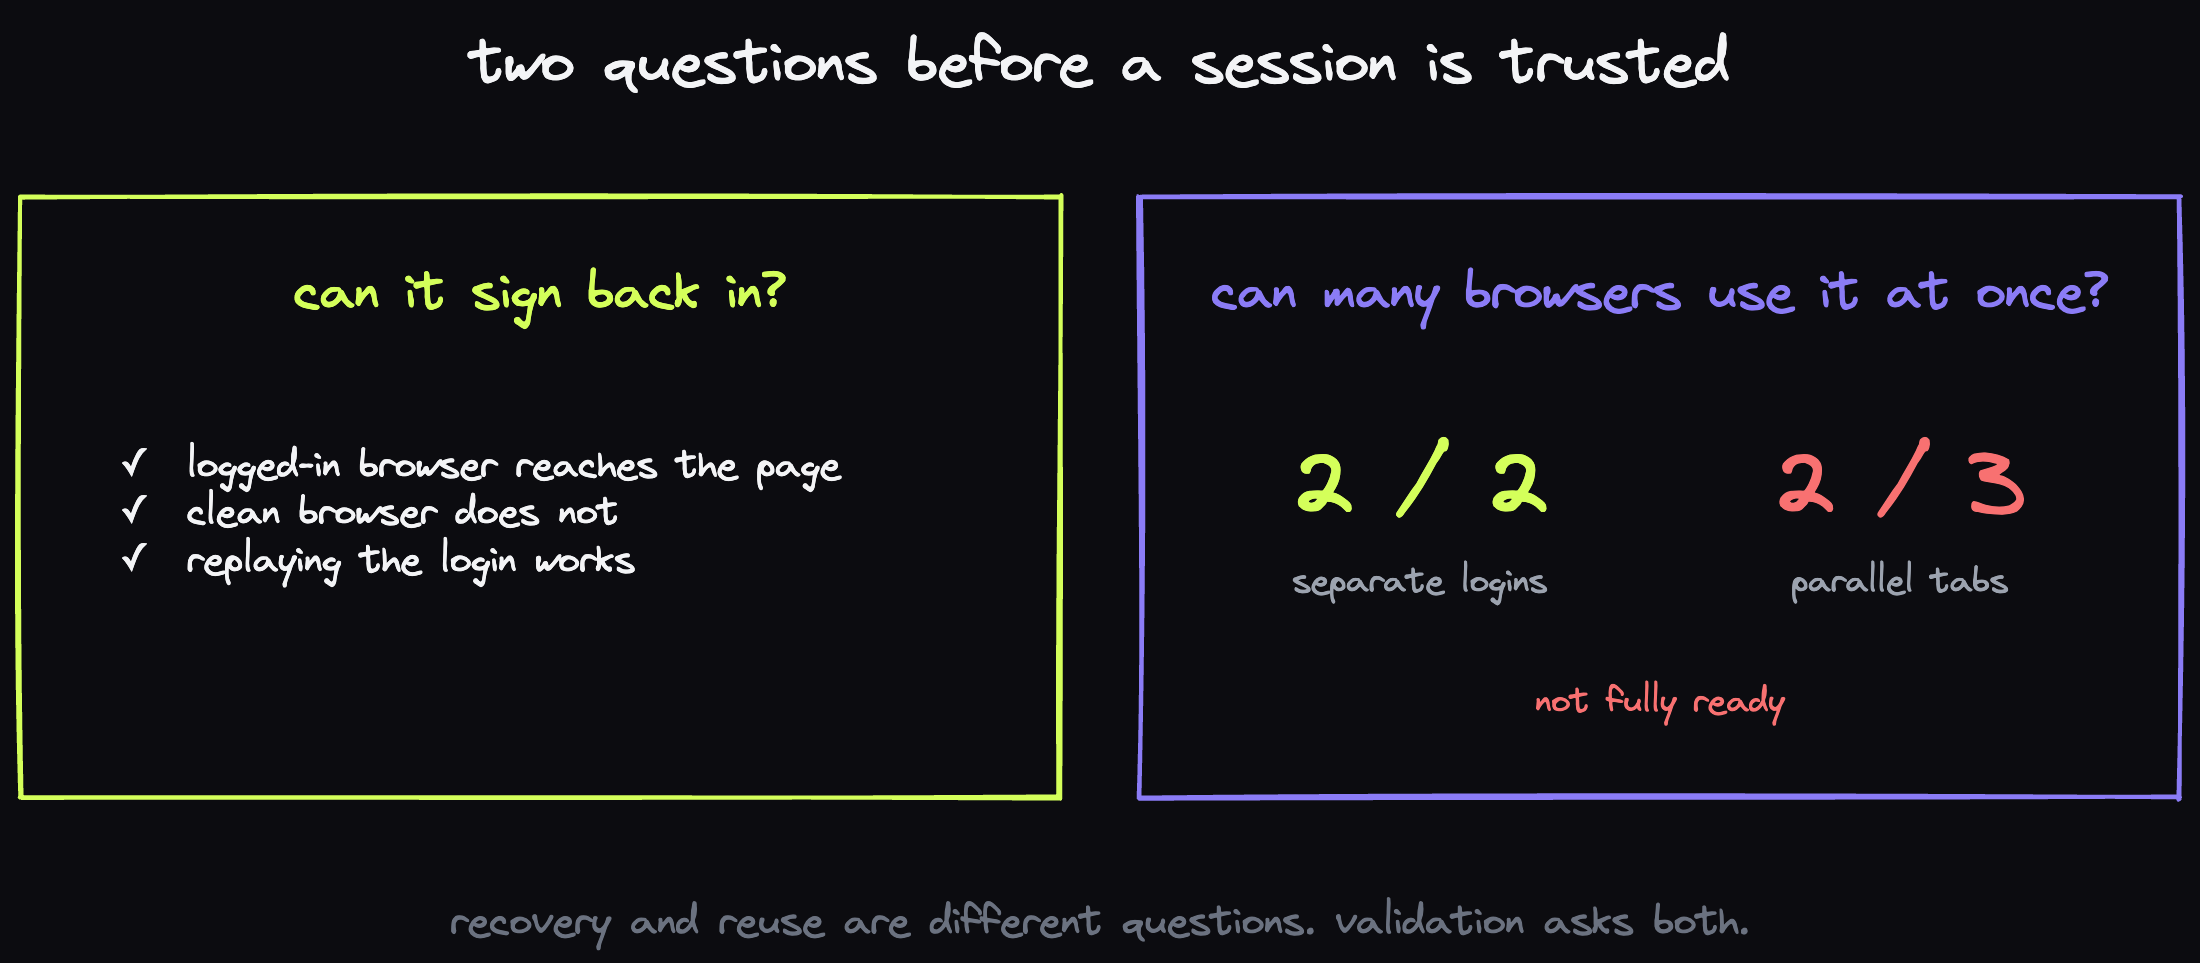
Recovery and reuse are different questions. Validation asks both.
